Linux commands[2]
Linux Links Soft links Aka Symbolic link It is a pointer to the original file Just like a shortcut in windows and smaller file size Different inode number If we delete the original file, the soft…

ON THIS PAGE
Linux Links
Soft links
-
Aka Symbolic link
-
It is a pointer to the original file
-
Just like a shortcut in windows and smaller file size
-
Different inode number
-
If we delete the original file, the soft links will become useless.
Syntax:
ln -s {path}/targetFile {path}/srcFileExample:
1.To link
ln -s /home/student/abc.txt /tmp/slabc.txt2.To unlink
unlink
unlink /tmp/slabc.txt
Hard Link
-
Different name of the same file
-
Same file size as original file
-
Same inode number
-
If the original file is deleted, the hardlinks will still contain the data that were in the
-
original file
Syntax:
ln {path}/targetFile {path}/srcFileExample:
1.To link
ln /home/student/xyz.txt /home/student/hlxyz.txt2.To unlink
unlink /home/student/hlxyz.txt
Inode
- It is a data structure in Unix that denotes a file or a directory on a file system.
- Every file in the system has an inode (Index node), (information node)
- Contains all file information except the file contents and name.
- It contains
a. Mode – permissions and file descriptor(file type, directory, no. of link,
block device)
b. Owner Information
c. Size
d. location of the file on the disk
e. Timestamp – creation & modification
f. Data Blocks – Pointers to the actual data - Just like a personal ID or a passport (Without a name)
- Each Inode has a number that is used in the index table.
- Linux kernel uses Inode number to access the contents of an Inode.
ls -i : To see the inode number
Packet Management
APT [Advanced Packaging Tool]
APT is a high level packet manager. Provides a way to retrieve and install packages including. Words with the package proper name. Does not work with deb that means it will not directly install .deb packages. Need to download them from the repository.
Commands
-
apt-get install [package_name] : To installs packages with dependencies.
-
apt-get remove [package_name]: To removes packages but no dependencies.
-
apt autoremove: removes packages installed but no longer required.
-
apt-get clean: To remove already installed downloaded packages for .deb software
-
apt-get purge [package_name]: combination of remove and clean.
-
apt-get update: Reads the /etc/apt/sources.list file and updates the system’s
database of packages available for installation -
apt-get upgrade: Upgrades all packages if there are updates available. Run this after running apt-get update.
-
Note: We can use only apt instead of apt-get. As in newer version only apt is also supported.
Important files related APT
-
ls /var/lib/apt/lists: To see list of installed packages
-
ls /var/lib/dpkg: To see the list of installed packages
-
dpkg -l: TO see the list of the packages on the device.
-
cat/var/lib/dpkg/status: To print status of all packages and see them in detail.
-
/etc/apt/sources.list: This file controls repositories from which APT constructs its database.
-
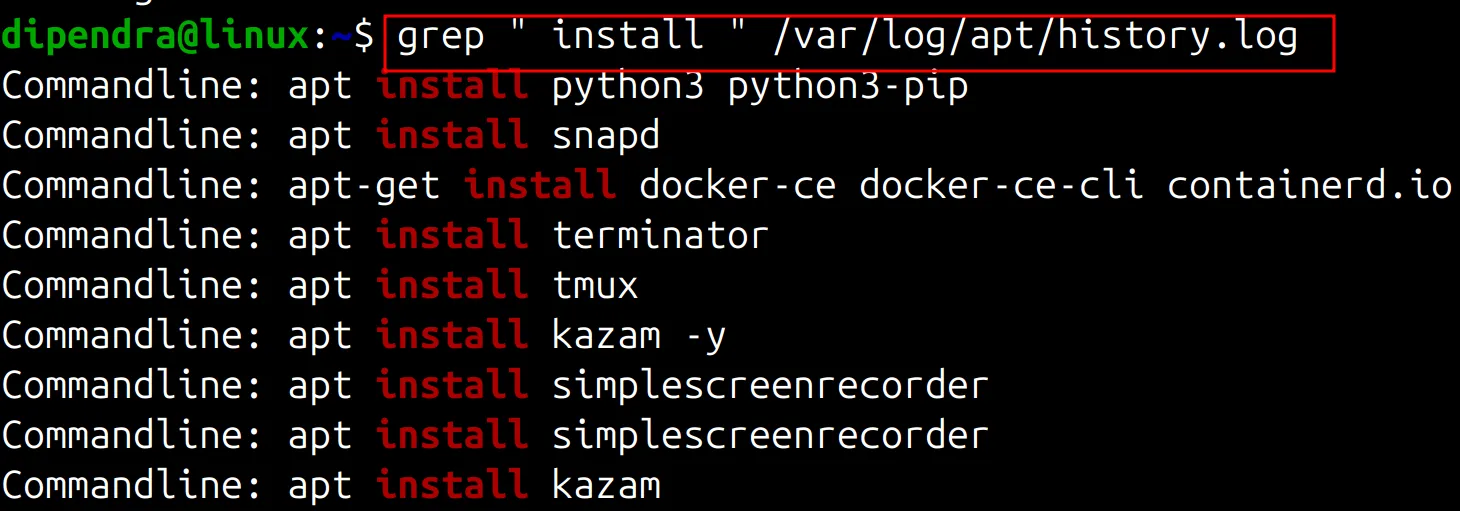
grep ” install ” /var/log/apt/history.log
- To see list of packages installed using apt install command
APT-CACHE
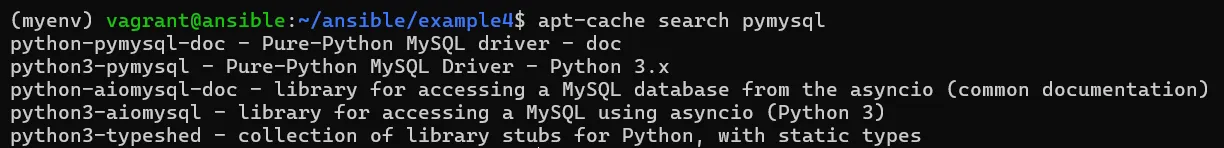
- apt-cache search [package_name]: Looks additional packages available. Useful when apt-get install fails.
- apt-cache show [package_name]: Shows dependency information, version numbers and a basic description of the package
Aptitude
Aptitude is high level package manager used to perform management tasks (installing, upgrading, and removing packages, also handling dependency resolution automatically.
>>aptitude update, aptitude install, aptitude remove, aptitude clean, or aptitude
purge are the same as the apt-get counterparts.
>>aptitude search or aptitude show is also same as the apt-cache counterparts.
dpkg
- dpkg is a low level package manager. It can install, remove, provide information about and build *.deb packages but it can’t automatically download and install their corresponding dependencies.
- dpkg -i install [package_file_name].deb: Installs a .deb file
- dpkg -l: Lists packages currently installed on the system.
- dpkg –configure package-name(s): Run a configuration interface to set up a package.
- dpkg-reconfigure package-name(s): Runs a configuration interface on an already installed package.
Users and Groups
Most beautiful feature of Linux OS is it allows multiple users[1000’s of the users] accessing the system at the same time. Provides security to protect each user from other permissions maintaining integrity and confidentiality.
Types of users

- Superuser or root user: The most powerful user/ administrator user.
- System users: They are created by the software or application, e.g when we install
apache, it creates apache user. - Normal user: users created by root user, only root has permission to create or remove the user
Whenever we create a new user in linux.
● A home directory is created for the user(/home/username)
● A mail box is created(/var/spool/mail)
● unique UID & GID are given to user
Files related to users and groups
| Passwd file /etc/passwd | /etc/shadow file |
|---|---|
| This file stores user related data. root:x:0:0:root:/root:/bin/bash ● root = name ● x = link to password file i.e /etc/shadow ● 0 or 1 = UID (user id) ● 0 or 1 = GID (group id) ● root or bin = comment (brief information about user) ● /root or /bin = home directory of the user ● /bin/bash or /sbin/nologin = shell | This file stores users’ password and password related information. Just like /etc/passwd file, this file also uses an individual line for each entry. root:*:19229:0:99999:7::: 1.Username 2.Encrypted password 3.Number of days when password was last changed 4.Number of days before password can be changed 5.Number of days after password must be changed 6.Number of days before password expiry date to display the warning message 7.Number of days to disable the account after the password expiry 8.Number of days since the account is disabled Reserved field |
Group file
/etc/group
The file /etc/group stores group information. Each line stores one group entry
User Commands
- adduser {username} :To add username with default parameters
- useradd : To add username with non-default parmeters.
- Options :
- -c: comment
- -d: home directory
- -m : create home directory
- -e : account expiry date
- -g : primary group
- -G : secondary group -s //shell
- -u: user id
- Example:
- useradd -c “Dipendra” -m -d /var/dipen-e 2023-01-05 -g staff -G hr,admin -s /bin/bash -u 2000 dipendra
- Options :
- useradd -D :Prints user default values [/etc/default/useradd] >>Default file
- usermod [option]: To modify the user
- Options
- -c
- -d
- -e
- -g
- -G
- -s
- -u
- -l
- usermod -l dipendra dipen
- –L
- usermod -L dipen
- -U
- usermod -U dipen
- Example:
- usermod -e 2023-01-30 -s /bin/sh -u 3000 dipen
- Options
- su username: To switch to the another user
- userdel username: To delete the user
- -r flag can be used to delete recursively.
- id username: To see details of the user
- groups username: TO see all the associated groups with user
- passwd username: To change password of the user
- echo $shell: To see the assigned shell to the user
- chage -l username: To see password related details
- chage username: To change password aging policies. we need to add them manually using the options displayed on the screen or,
- we can use -option to use different options.ie;
- -m
- -M
- -W
- -I
- -E <Date to set A/c expiry date>
- Example:
- chage -m 1 -M 14 -W 2 -I 3 -E 2023-02-02 dipen
- we can use -option to use different options.ie;
- last: Gives user who logged into the system
- who: Currently logged in user
- lsof: Gives all the open files by the user
Group commands
- Syntax:[groupadd ]
- Ex: groupadd staff
- Note: Group changes can be done by editing group files.ie; /etc/group
File permissions
In Linux we set permissions in files/directories so that people can only perform the tasks which permission we are allowing.
Read: Allows to view the contents of a file and allows to list contents of a
directory.
Write: Allows to modify contents of a file and allows create and remove,
editing contents of a directory.
Execute: Allows to run a file or execute a program/ script and allows you to
change directory and make it your working directory, allows long listing.
-: No permission

Changing permissions
- Syntax chmod [permission_type] [File/Directories] ; -R for recursive.
- chmod 644 filename: TO give owner read, write permissions and to group and other only read permission.
- chmod -R 755 /path/filename: Grants full permission to owner and read, execute permission to others
- This can be used when we need to alter to single permission only and leaving others as it is.
- chmod o-x /path/filename: Removing execute permission from others
- chmod u+x /filename: Granting execute permission to user
Changing ownership of file
- syntax: chown [Username] [File/Directories] ;-R is for recursive
- chown -R dipen /home/dipen/testdir1
Changing group ownership for file/dir
- syntax: chgrp [Group name] [File/Directories] ;-R for recursive
- chgrp -R testgroup1 testdir1
Managing file and group ownership simultaneously
- syntax: chown username:groupname [File/Directories] ;-R for recursive
- chown -R apache:apache /data/dipen.com.np
- a dot (.) can be used instead of colon (:)
Special permission
Sticky-bit
If a sticky bit is set on a directory then only the owner can delete their own
file/directory.
syntax:
chmod 1775 dirname: Here 1 is sticky bit.
SUID-bit
SUID-bit, setuid bit let’s to run commands on the behalf of other users.
syntax:
chmod u+s /usr/bin/ls ;To add suid bit to the command
chmod u-s /usr/bin/ls ;To remove the suid bit from the command
SGID Bit
If SGID-bit is set on a directory, then any files/directory created inside that
directory will inherit group ownership of that directory
syntax:
chmod g+s filename/dirname
Archiving and Compressing
Archiving:
The process of combining multiple files and folder into a single file is known as achieving. The process doesn’t reduce the size of the files instead it simplifies storage and transfer by consolidating them.
Tools used:
tar: Widely used in Linux
zip: Combines using archiving and compression.
commands:
- tar -cvf tarname.tar muliples_files/directories :To create tar file
- c: create
- v:verbose
- f: to specify the file
- z: can be used to do both compress and archieve
- syntax: tar -czvf tarname.tar.gzip muliples_files/directories
- tar xvf tarfile.tar: To extract the tar file
- tar xzvf tarname.tar.gzip: To extract compressed tar file
Compression
Reduces the size of the files by encoding file data using algorithms that eliminate redundancy.
Tools: gzip,hzip,xz
Commands
- zip -r filename.zip targetdirectory : To zip the file. Here -r means recursively. IF we don’t use -r it will create the zip file but that file will eb empty.
- Example: zip -r hello.zip testdirectory
- unzip filename: To unzip the file
Sudo
Sudo gives the power to a normal user to execute commands which are
owned by the root user.
sudo su: To switch to the root user but you directory path is the same in which you are
sudo -i: To switch to root user home directory.
To give user sudo privelage
- We can directly add user to the sudo group.
- vim /etc/group and add username in sudo group here. OR
- usermod -aG sudo username
- usermod -aG admin username #Admin group also have sudo privelage
- visudo :We can also use this to give sudo privilege and configure a lot more about them but the safer way to add user to sudoers.d directory and in /etc/sudoers.d/filename file. And in this file we can configure the what he can when switching to sudo.
- About this file: These are already in the visudo file. We just need to modify them.
- host alias: To create host groups
- User_Alias: To create alias of the user
- User_Alias TRUSTED=rabindra,pankaj
- Cmnd_Alias: TO create the alias of the commands
- Cmnd_Alias LIMITED=/usr/sbin/useradd,/usr/bin/passwd
- Now we can give permission to the user by sing this alias.ie:
- TRUSTED ALL=ALL,!LIMITED
- For groups: %groupName ALL=(ALL) NOPASSWD:ALL
- root ALL=(ALL:ALL) ALL
- The first field indicates the username that the rule will apply to (root).
- First “ALL” indicates that this rule applies to all hosts.
- Second “ALL” indicates that the root user can run commands as all users.
- Third “ALL” indicates that the root user can run commands as all groups.
- Fourth, “ALL” indicates these rules apply to all commands.
- Example:
- dipen ALL=(ALL:ALL) /usr/bin
- dipen ALL=(ALL:ALL) !/usr/bin/apt,/usr/bin/df
- vagrant ALL=(ALL) NOPASSWD:ALL :To set no password for all commands
- About this file: These are already in the visudo file. We just need to modify them.
Processes
top
The top command is a real-time system monitoring tool in Linux that provides a dynamic, interactive view of a system’s running processes. It displays system summary information and a list of processes or threads currently managed by the Linux kernel.
-
top – 04:10:44 up 1 day, 2:41, 3 users, load average: 0.09, 0.09, 0.06
- Here up means up time
- users: No of user currently logged in
- load average: Load given to the cpu
- 0.09: System load for the last 1 minutes.
- 0.09: System load for the last 5 minutes.
- 0.06: System load for the last 15 minutes.
- Note: Value nearest to zero means the CPU is not overloaded and the higher value indicates CPU overload/congestion .
-
Tasks: 196 total, 1 running, 195 sleeping, 0 stopped, 0 zombie
- total: Total number of processes.
- running: Number of currently active processes.
- sleeping: Processes waiting for input/output.
- stopped: Processes stopped manually.
- zombie: Zombie processes (terminated but still in the process table).
-
%Cpu(s): 0.2 us, 0.5 sy, 0.0 ni, 99.3 id, 0.0 wa, 0.0 hi, 0.0 si, 0.0 st
- us (User CPU): CPU time spent on user processes.
- sy (System CPU): CPU time spent on kernel processes.
- ni (Nice CPU): CPU used by processes with a nice priority.
- id (Idle CPU): Idle CPU (higher is better).
- wa (Wait I/O): CPU waiting for I/O (disk/network operations).
- hi (Hardware IRQ): CPU used by hardware interrupts.
- si (Software IRQ): CPU used by software interrupts.
- st (Steal Time): CPU stolen by hypervisor in virtualized environments
-
MiB Mem : 3843.4 total, 1682.4 free, 1658.1 used, 735.4 buff/cache
- total: Total RAM.
- free: Unused RAM.
- used: RAM actively used by processes.
- buff/cache: Memory used for buffers and cache.
-
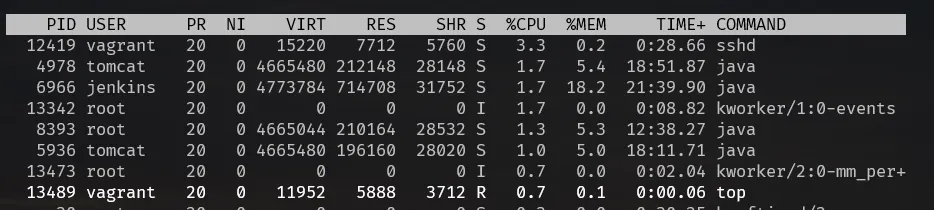
PID: Process ID.
-
USER: Owner of the process.
-
PR (Priority): Process scheduling priority.
-
NI (Nice Value): Process priority adjustment (-20 to 19, lower is higher priority).
-
VIRT (Virtual Memory): Total memory used (includes swap).
-
RES (Resident Memory): Actual memory used (without swap).
-
SHR (Shared Memory): Memory shared with other processes.
-
S (State):
- R: Running
- S: Sleeping
- T: Stopped
- Z: Zombie
-
%CPU: CPU usage.
-
%MEM: Memory usage.
-
TIME+ : Total CPU time used
-
Using TOP press
- q: Exit top.
- h: Display help menu.
- k: Kill a process by PID.
- M: Sort by memory usage.
- P: Sort by CPU usage.
- T: Sort by process run time.
- Shift + R: Reverse sort order.
Process status(ps)
The ps command in Linux is used to display information about active
processes. It provides details such as process IDs (PIDs), CPU usage,
memory consumption, and other key attributes of running processes
- ps aux
- a – Show processes of all users
- u – Displays user-oriented format
- x – List processes without a controlling terminal
- Displays all running processes on the screen and quits. Process in [ ] are called kernel threads
- ps -ef
- e – show all processes
- f – display full format(more details)
- Example:
- ps -ef | grep apache2
- Kill process
- kill (pid)
- Kill -9 (pid): kill forcefully
- Example:
- ps -ef | grep apache2 | grep -v ‘grep’ | awk “{print $2}” | xargs kill -9
- ps -u username: Displays processes owned by a specific user
- ps -T -p: Show threads of a process
- T – display threads
- p – process id
- ps aux –sort=-%mem: Sorts by memory usage (highest first)
- ps aux –sort=-%cpu: Sorts by CPU usage (highest first).
Zombie: Processes whose operations are done but their entry is still in the process
table.
Orphan: A child process that remains running even after it;s parent process is
terminated or completed without waiting for the child process execution
- Difference between Apache web server and nginx web server
- To install apache2
- Commands
- Apache2 configuration overview
- To load a website in apache2
Shell Scripting
- Writing our first script
- Variable
- To take input from user we use
- Positional Argument
- Command substitute
- If
- For
- While
- To see Ip address of the machine
- Systemctl commands
- Change directory [cd]
- Listing command [ls]
- Basic commands
- Copy command
- Move command
- Remove Command
- To get help and see suggestion in linux
- To view/print contents of file
- Grep
- Sed [Stream Editor]
- Cut
- AWK
- VIM
- Input/Output redirection
- To download using links
Linux Introduction
- Overview
- Architecture
- Linux Terminology
- Linux File Structure
- / – Root
- /bin – User Binaries.
- /sbin – System Binaries
- /etc – Configuration Files
- /dev – Device Files
- /proc – Process Information
- /var – Variable Files
- /tmp – Temporary Files
- /usr – User Programs
- /home – Home Directories
- /boot – Boot Loader Files
- /lib – System Libraries
- /opt – Optional Add-on Applications
- /mnt – Mount Directory
- /media – Removable Media Devices
- /srv – Service Data
- Interface and logging in via terminal
- Linux File system
Keep reading
- Shell Scripting
It is a way to automate tasks by writing a series of commands in a text file called script that Linux shell can execute. It’s like creating a ‘to do list’ for your computer to follow step by step…
- Linux Commands
To see Ip address of the machine ip addr show :Shows all the interfaces ip ip -4 addr show: Show only ipv4 address ifconfig: Same as ip addr show but it needs net tools to show ip address. Systemctl…
- Apache web server
The Apache HTTP server, commonly known as Apache is a free and open-source web server, that delivers web content through the internet. As open-source software, its original source code is freely…